Your whole security program.
One AI control plane.
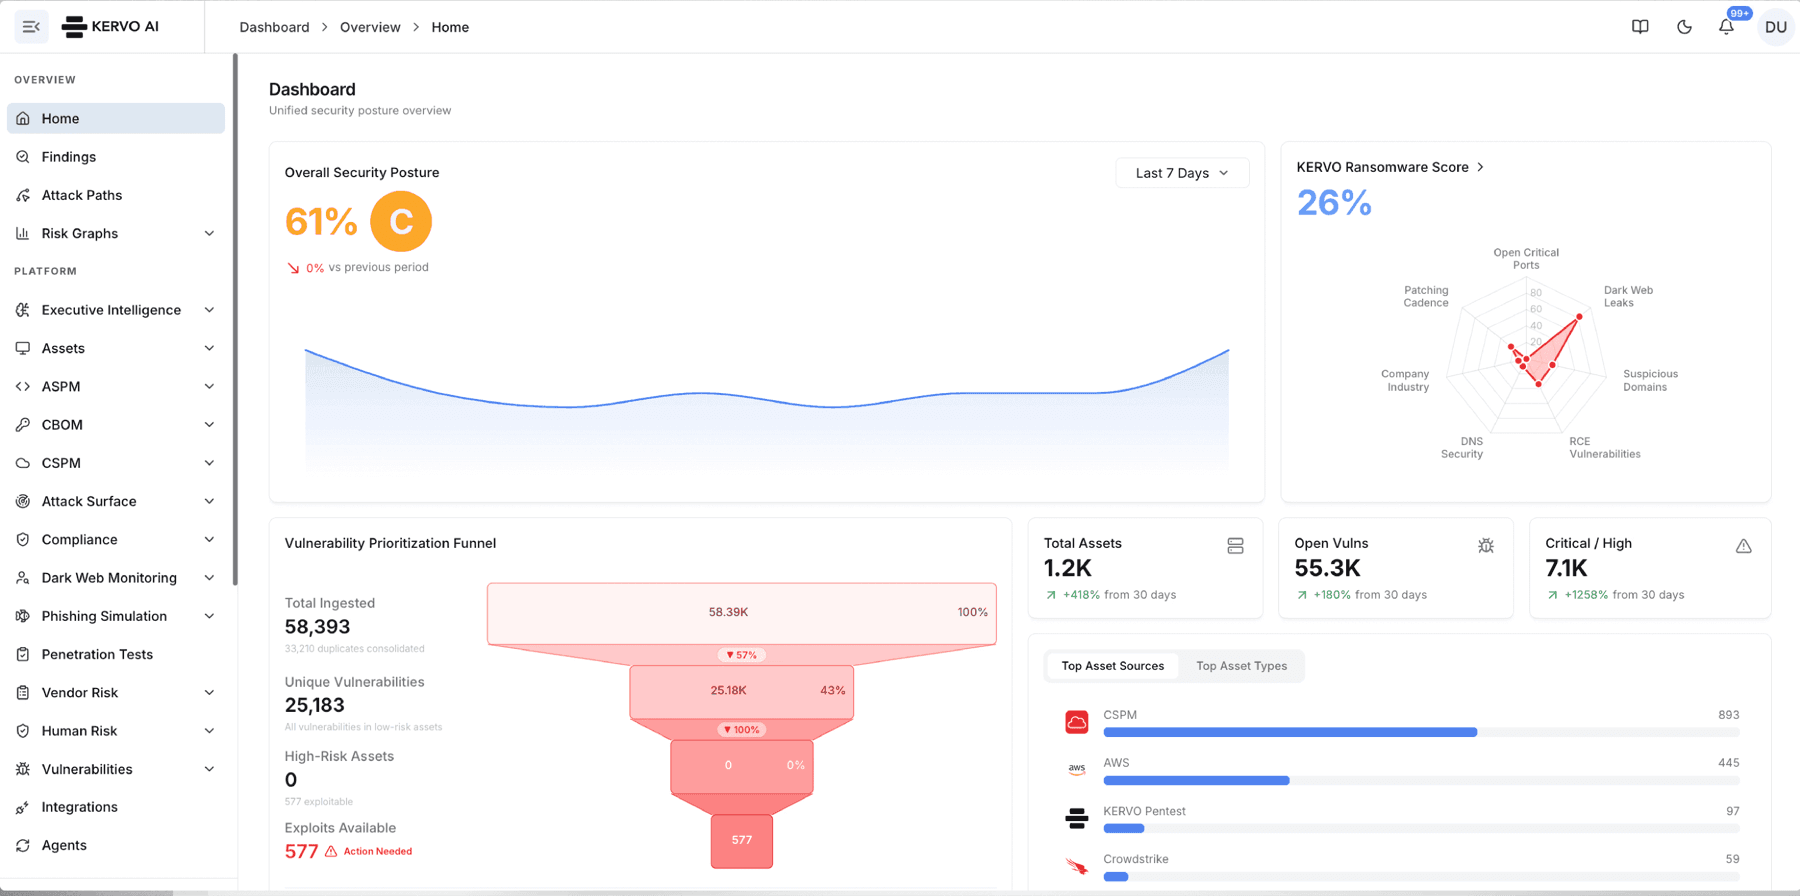
A complete AI security team on one data model. Its agents find every asset, rank what attackers can reach, fix it and keep you audit-ready.

Security is one job. Most teams run it in pieces.
Discovery, prioritisation, investigation and evidence each live in a different tool. The seams between them are where incidents start. Kervo AI runs it all as one system.
Five stages. One loop. It never stops.
Built to close the gaps between tools.
Discovery to audit evidence on one data model. Fix what matters first, and prove it.
Attack Surface Discovery
Every device, cloud resource, app and vendor in one live inventory, including the ones nobody wrote down.
Attack-Path Intelligence
Exposures chained into the routes an attacker would actually take.
Risk-Based Prioritization
Findings ranked by exploitability and business impact. A short list, with a reason on every line.
- Reachable · from internet
- Exploit · public PoC
- Attack path · AP-118
AI Analyst
Investigates every finding, works out the fix and pushes it once you approve.
Continuous Compliance
Evidence collects itself and maps across SOC 2, ISO 27001, GDPR, NIS2 and more.
Dark Web & Vendor Risk
Leaked credentials, lookalike domains and vendor exposures, tracked as attack surface.
It works because it's one system underneath.
Suites built by acquisition share a login, not a data model. Kervo AI was built as one system, so every signal from all five stages correlates on its own.
Connected in minutes, full picture in 48 hours
Read-only API connections, no agents for most coverage. First findings within hours.
One data model, every correlation
CVEs, misconfigurations, leaked credentials and vendor exposures live together, so attack paths draw themselves.
Ten priorities, not 3,000 findings
The risks that matter today, with what's at stake and what to do first.
Your whole program, however your team is built.
Run your whole security function in Kervo AI, with AI agents doing the work a team of ten can't.
Run everything in Kervo AIKeep the tools you've standardised on. Kervo AI correlates them into one risk picture, with AI agents working alongside your analysts.
Connect your stack Acunetix
 AWS
 Azure
 Burp Suite
 CrowdStrike
 Fortify SCA
 GitHub
 GitLab
 Google Cloud
 Jira
 JumpCloud
 Kervo AI Network Scanner
 Mend.io
 Microsoft Defender
 Microsoft Teams
 Nessus
 Nmap
 OpenVAS
 Oracle Cloud
 OWASP ZAP
 Palo Alto Cortex XDR
 Qwiet AI
 Rapid7
 Semgrep
 Slack
 SonarCloud
 SonarQube
 Sophos XDR
 SVN
 WPScan
The questions buyers ask first.
What is an AI control plane for security? Is Kervo AI just orchestration on top of other tools?
A control plane sees the state of everything, decides what matters and drives the response. Kervo AI is that layer, and it owns the data plane too: it scans, evaluates and resolves natively. For a lean team it can be the whole security function. For an established team it sits above the tools you run and puts AI agents to work alongside your analysts.
What do the five stages mean?
Know, Evaluate, Resolve, Validate, Orchestrate: discover it, weigh it, fix it, prove it, run it. Most tools own one stage. Kervo AI runs all five on one platform, so security runs as one continuous loop instead of five disconnected purchases.
How is this different from the big platforms already out there?
Most were assembled by acquisition: separate products behind one login, separate data models underneath. Kervo AI was built as one system. That single data model is what lets a dark web leak, a CVE and a cloud misconfiguration correlate on their own.
We're a small team. Is this too much platform for us?
Small teams suffer most from disconnected tools, because nobody can staff a specialist per tool. For one to ten people, Kervo AI can be the whole security function, with AI agents doing the investigation, evidence and reporting work.
We already have a mature stack. Why add another platform?
Your tools each hold a piece of the picture. Kervo AI connects to them, pulls their data into one model and correlates it into the posture no single tool can show. You keep every investment and gain the control plane above it.
See your real risk,
not a demo tenant.
We connect read-only to your environment and show what's actually there: attack paths, coverage gaps and compliance position.